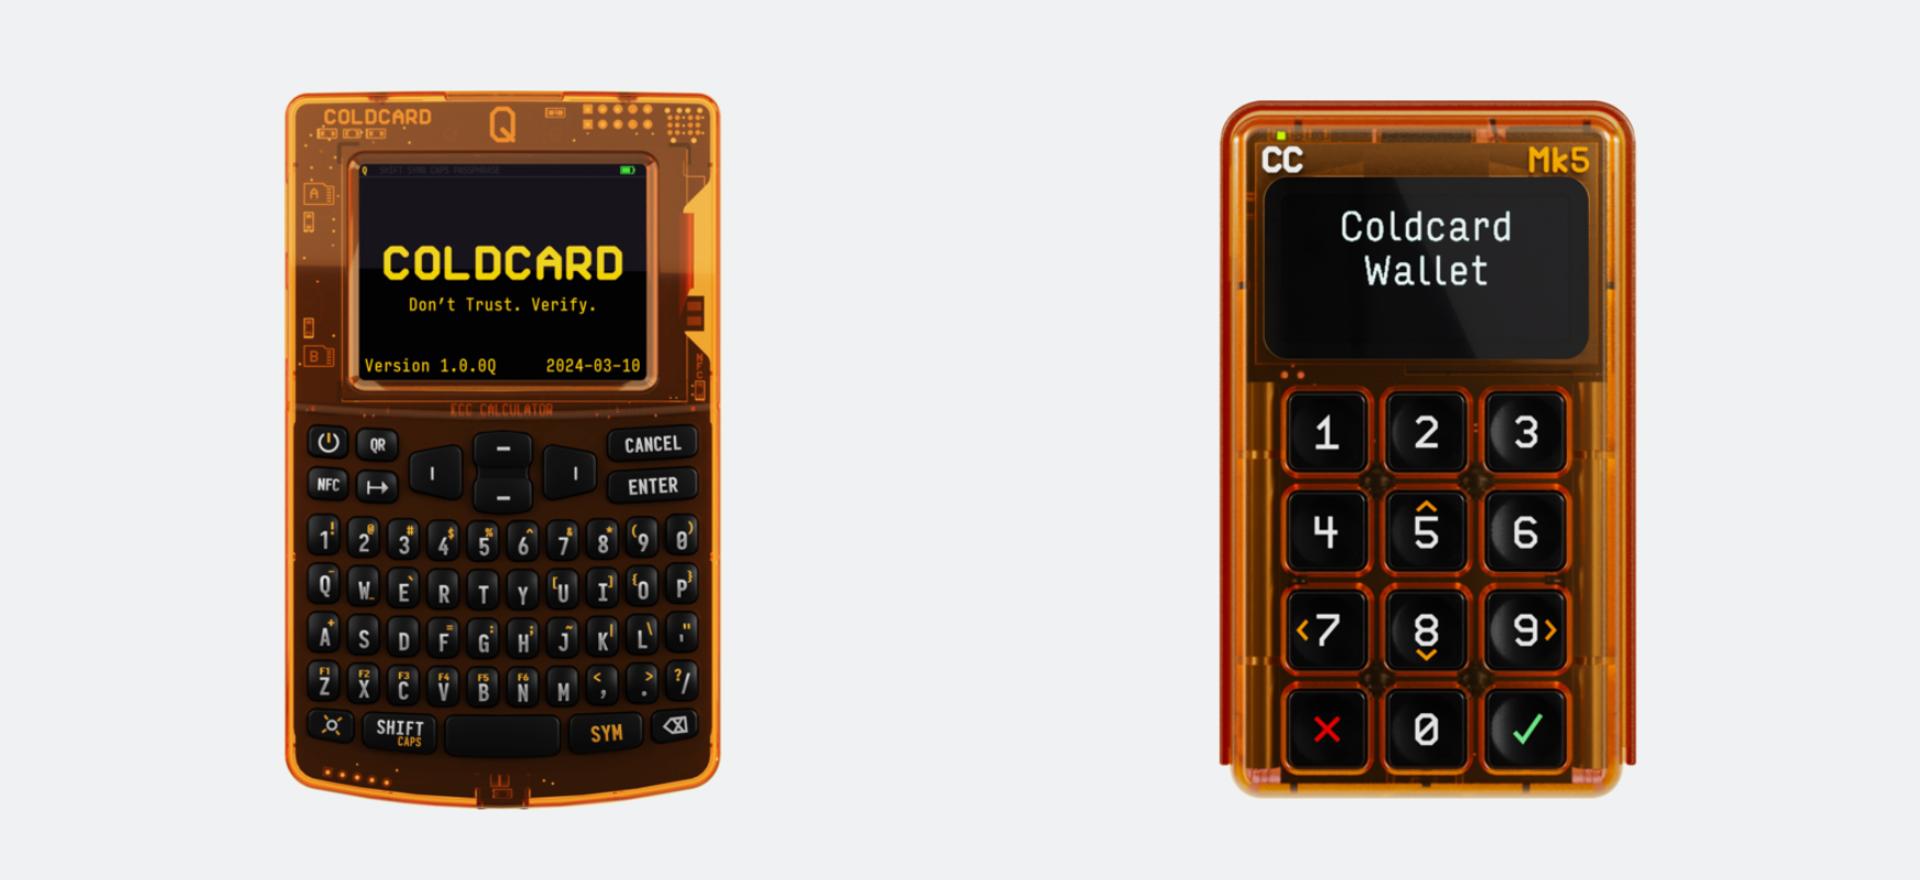
Coldcard released new firmware following a major security breach that resulted in $114 million in stolen bitcoin. The update addresses vulnerabilities discovered during an intensive three-week review period, though the company clarified that the patch does not restore security to already-compromised wallets.
The theft exploited a flaw in Coldcard's hardware wallet that attackers leveraged to drain user funds. The exact mechanism remains unclear from public disclosures, but the scale of the loss triggered an immediate security audit. Coldcard's development team conducted an exhaustive code review to identify additional weaknesses beyond the initial vulnerability.
The review process proved valuable beyond fixing the original exploit. Developers uncovered separate bugs that posed independent risks to user security. These additional flaws likely would have remained undetected without the intensive post-breach audit. Coldcard attributed some of these discoveries to AI-assisted code analysis, suggesting the company deployed machine learning tools to scan for patterns indicative of common vulnerabilities.
This approach reflects a broader trend in hardware wallet security. Vendors increasingly rely on automated tools alongside traditional human review to catch subtle bugs before they reach production. AI systems excel at identifying consistency issues, memory safety problems, and logic errors that human reviewers might miss during fatigue or time pressure.
The firmware update addresses multiple threat vectors. However, Coldcard issued a crucial warning: users whose wallets were already compromised cannot recover security through a simple update. Once private keys or seed phrases are extracted, updating the device's firmware provides no protection. Compromised users need to create entirely new wallets and transfer remaining funds to fresh addresses controlled only by them.
This distinction matters legally and operationally. Users who lost bitcoin cannot treat the firmware patch as a recovery tool. They must treat compromised wallets as permanently poisoned. The update benefits future users and protects against similar exploits, but it cannot undo past theft.
The Coldcard incident underscores the tension between hardware wallet security and user responsibility. Hardware wallets occupy a middle ground between full custody and exchange-based holding. They reduce counterparty risk compared to centralized platforms, but they remain vulnerable to manufacturing flaws, supply chain attacks, and firmware bugs. The $114 million loss demonstrates that hardware alone cannot guarantee safety if the software executing on that hardware contains exploitable vulnerabilities.
Coldcard faces reputational damage despite moving quickly to patch the flaw. Users who lost funds may pursue legal action against the company, arguing negligent security practices allowed the theft. The company's prompt response and use of AI-assisted analysis might mitigate liability, but it does not restore lost bitcoin.
The firmware release also signals that Coldcard intends to continue operating and maintaining its product. Companies facing major security breaches sometimes cease operations or face regulatory pressure that forces shutdown. Coldcard's decision to ship an update and publicly address the incident suggests the company plans to remain competitive in the hardware wallet market.
Users holding bitcoin on Coldcard devices should update immediately to receive the security fixes, even though the update cannot protect previously compromised assets. Future transactions and holdings benefit from the improved code. For those affected by the theft, the path forward requires abandoning affected wallets entirely and moving funds to demonstrably secure alternatives.